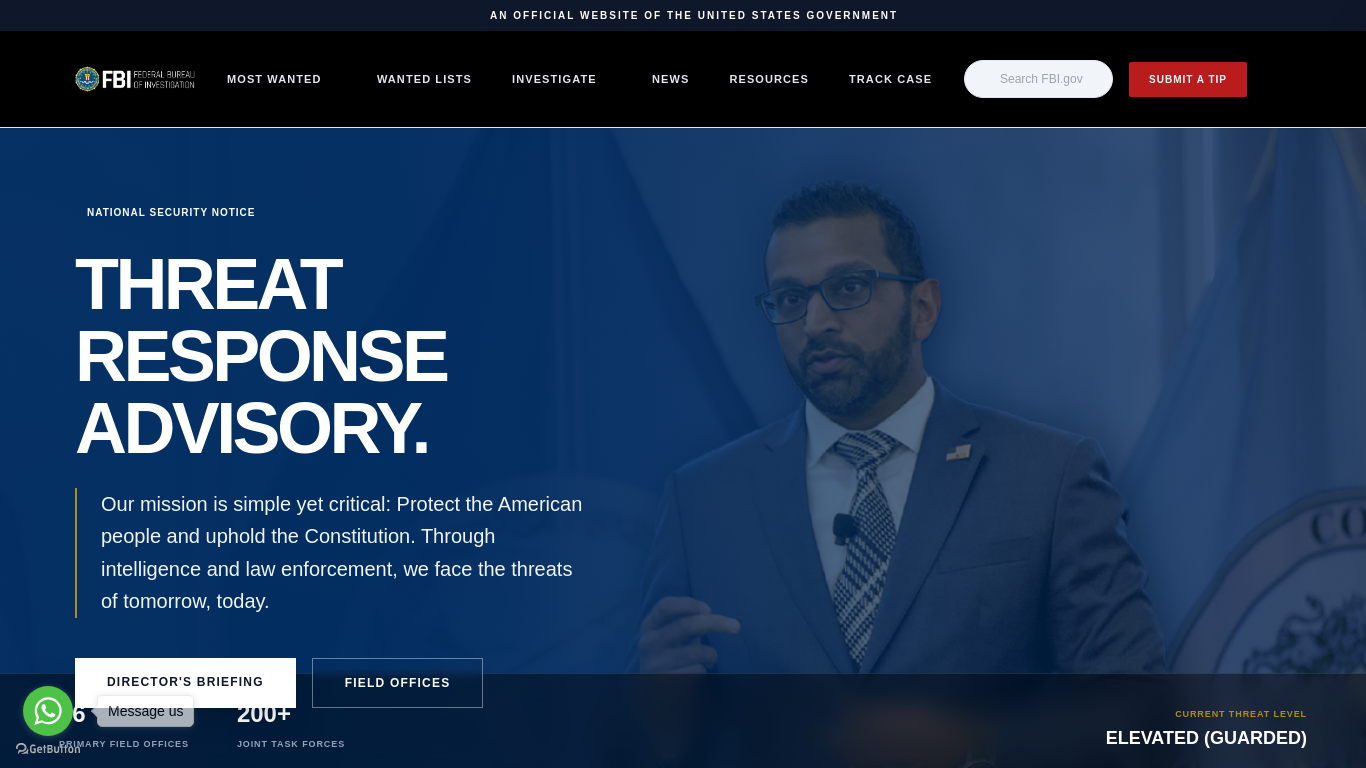
fbiinvdep.
Is it trustworthy?
Do not trust it.
PhishDestroy flags it as fraudulent. Do not pay or enter your details here.
- Suspicious TLD (.online)
Independent analysis by desenmascara.meAnalyzed Oct 07, 2026, 05:46 AMInvestmentMethodology
Not convinced by the verdict? Request a manual reviewRisk score: high probability of fraud
DangerousThis website appears to be fraudulent. Do not enter personal data or make purchases.
Why this verdict
Blocklist (PhishDestroy)This domain appears in DestroyList, the curated phishing feed maintained by PhishDestroy (PhishDestroy.io), so it remains classified as FRAUDULENT. At the time of this inspection, the site does not appear to be actively serving phishing content: the current page has minimal content and does not show an active campaign. The technical metadata shown below comes from direct site inspection. Curated match: fbiinvdep.online. Source: https://raw.githubusercontent.com/phishdestroy/destroylist/main/list.json
Analysis dossier
0checks run on this site
Cross-referenced against 150,000+ analysed domains · 1 finding
One deeper check is still locked: reading the page itself
- Reading the siteWe downloaded its code and visible contentDone
- Security certificate (SSL)Is it valid, or will the browser warn of an insecure connection?Clear
- Verified-domain listIs this a site we have already confirmed as legitimate?Clear
- Trust sealsTrusted Shops, Trustpilot, Confianza Online, Authorize.NetClear
- Global traffic rankingIs it among the million most visited sites?Clear
- Regulator warningsCNMV, FCA, SEC and other financial supervisorsClear
- Google Safe BrowsingGoogle's malware list (it does not cover scams)Clear
- Flagged by CloudflareDoes Cloudflare block the site for phishing?Clear
- PhishDestroy curated listPhishing domains confirmed by researchersFinding
- Scam-kit signaturesIs it built with a known phishing kit?Clear
- Hidden AI trapsInvisible instructions aimed at automated agentsClear
- ClickFix lureFake 'verify you are human' prompt asking you to run a commandClear
- Government impersonationDoes it pose as a public administration?Clear
- Cross-check with our historyWhat we already know about its page, server and ageClear
- Risk scoreThe final number, from 0 to 100Done
You know it is not safe. Now, why.
The verdict does not change. What you get is the method laid bare — what it promises, who it impersonates, how it walks you to the payment — and a report you can show your bank, the police, or whoever recommended it.
- The method, laid bareReads the whole site and reconstructs how the deception works, step by step, in its own words.
€0.60 per analysis. No account needed: pay and the verdict loads. Credits, not a subscription — no renewal, and a credit is spent only if the AI actually runs.
Report summary and questions
Analysis summary
We analysed fbiinvdep.online on October 6, 2026 and classified it as fraudulent (95/100). Based on its content, the site falls under “Investment”. The domain had been registered for about 6 months when we analysed it. It is registered through Dynadot Inc. Its server's IP address hosts 155 sites we flagged as fraudulent or suspicious in the last 30 days.
Frequently asked questions
- Is fbiinvdep.online legit?
- No. Our analysis of October 6, 2026 classified it as fraudulent. Do not send it money or personal details.
- Is fbiinvdep.online a scam?
- What we found are the signs of a fraudulent site; the detail is in this report. If you were contacted from this site, be wary.
- I already paid or shared my details. What should I do?
- Contact your bank as soon as possible to try to block or reverse the payment, and report it to the police. Change any passwords you gave; if you sent ID documents, watch for identity theft.
- Can this result change?
- Yes. It is a dated assessment and we keep every version of the report. If you run this site and think it is wrong, you can dispute it for free.
desenmascara.me flagged this domain as malicious in VirusTotal's global threat database. Tap to view the VT report.
14 signals unmasked
Analysis findings
Verified technical and public-source evidence for this domain.
Analysis time: 8.88s
0 to 100 — the higher, the riskier.
Possible scam farm / fraud cluster on this IP.
Google tracks malware and known phishing, not scams, so fraudulent shops often go unlisted.
Source: openai
People reported where they encountered this domain. Upgrade to Startup to see the channel breakdown.
Analysis history and previous reports
- Oct 07, 2026, 05:46 AMOpenFraudulent
- Oct 06, 2026, 05:37 PMDecided by: AI analysisSuspicious
Request a human review
24h · Public verdictA professional reviews the context, supporting evidence and external sources. The public verdict may confirm, qualify or correct this assessment; payment does not guarantee validation.
Next steps
Stay protected
Save the report, preserve the evidence, and share the finding with the right stakeholders.
Community experience
0 reportsShare your experience to help others. Reputation starts neutral and changes with positive or negative reports.